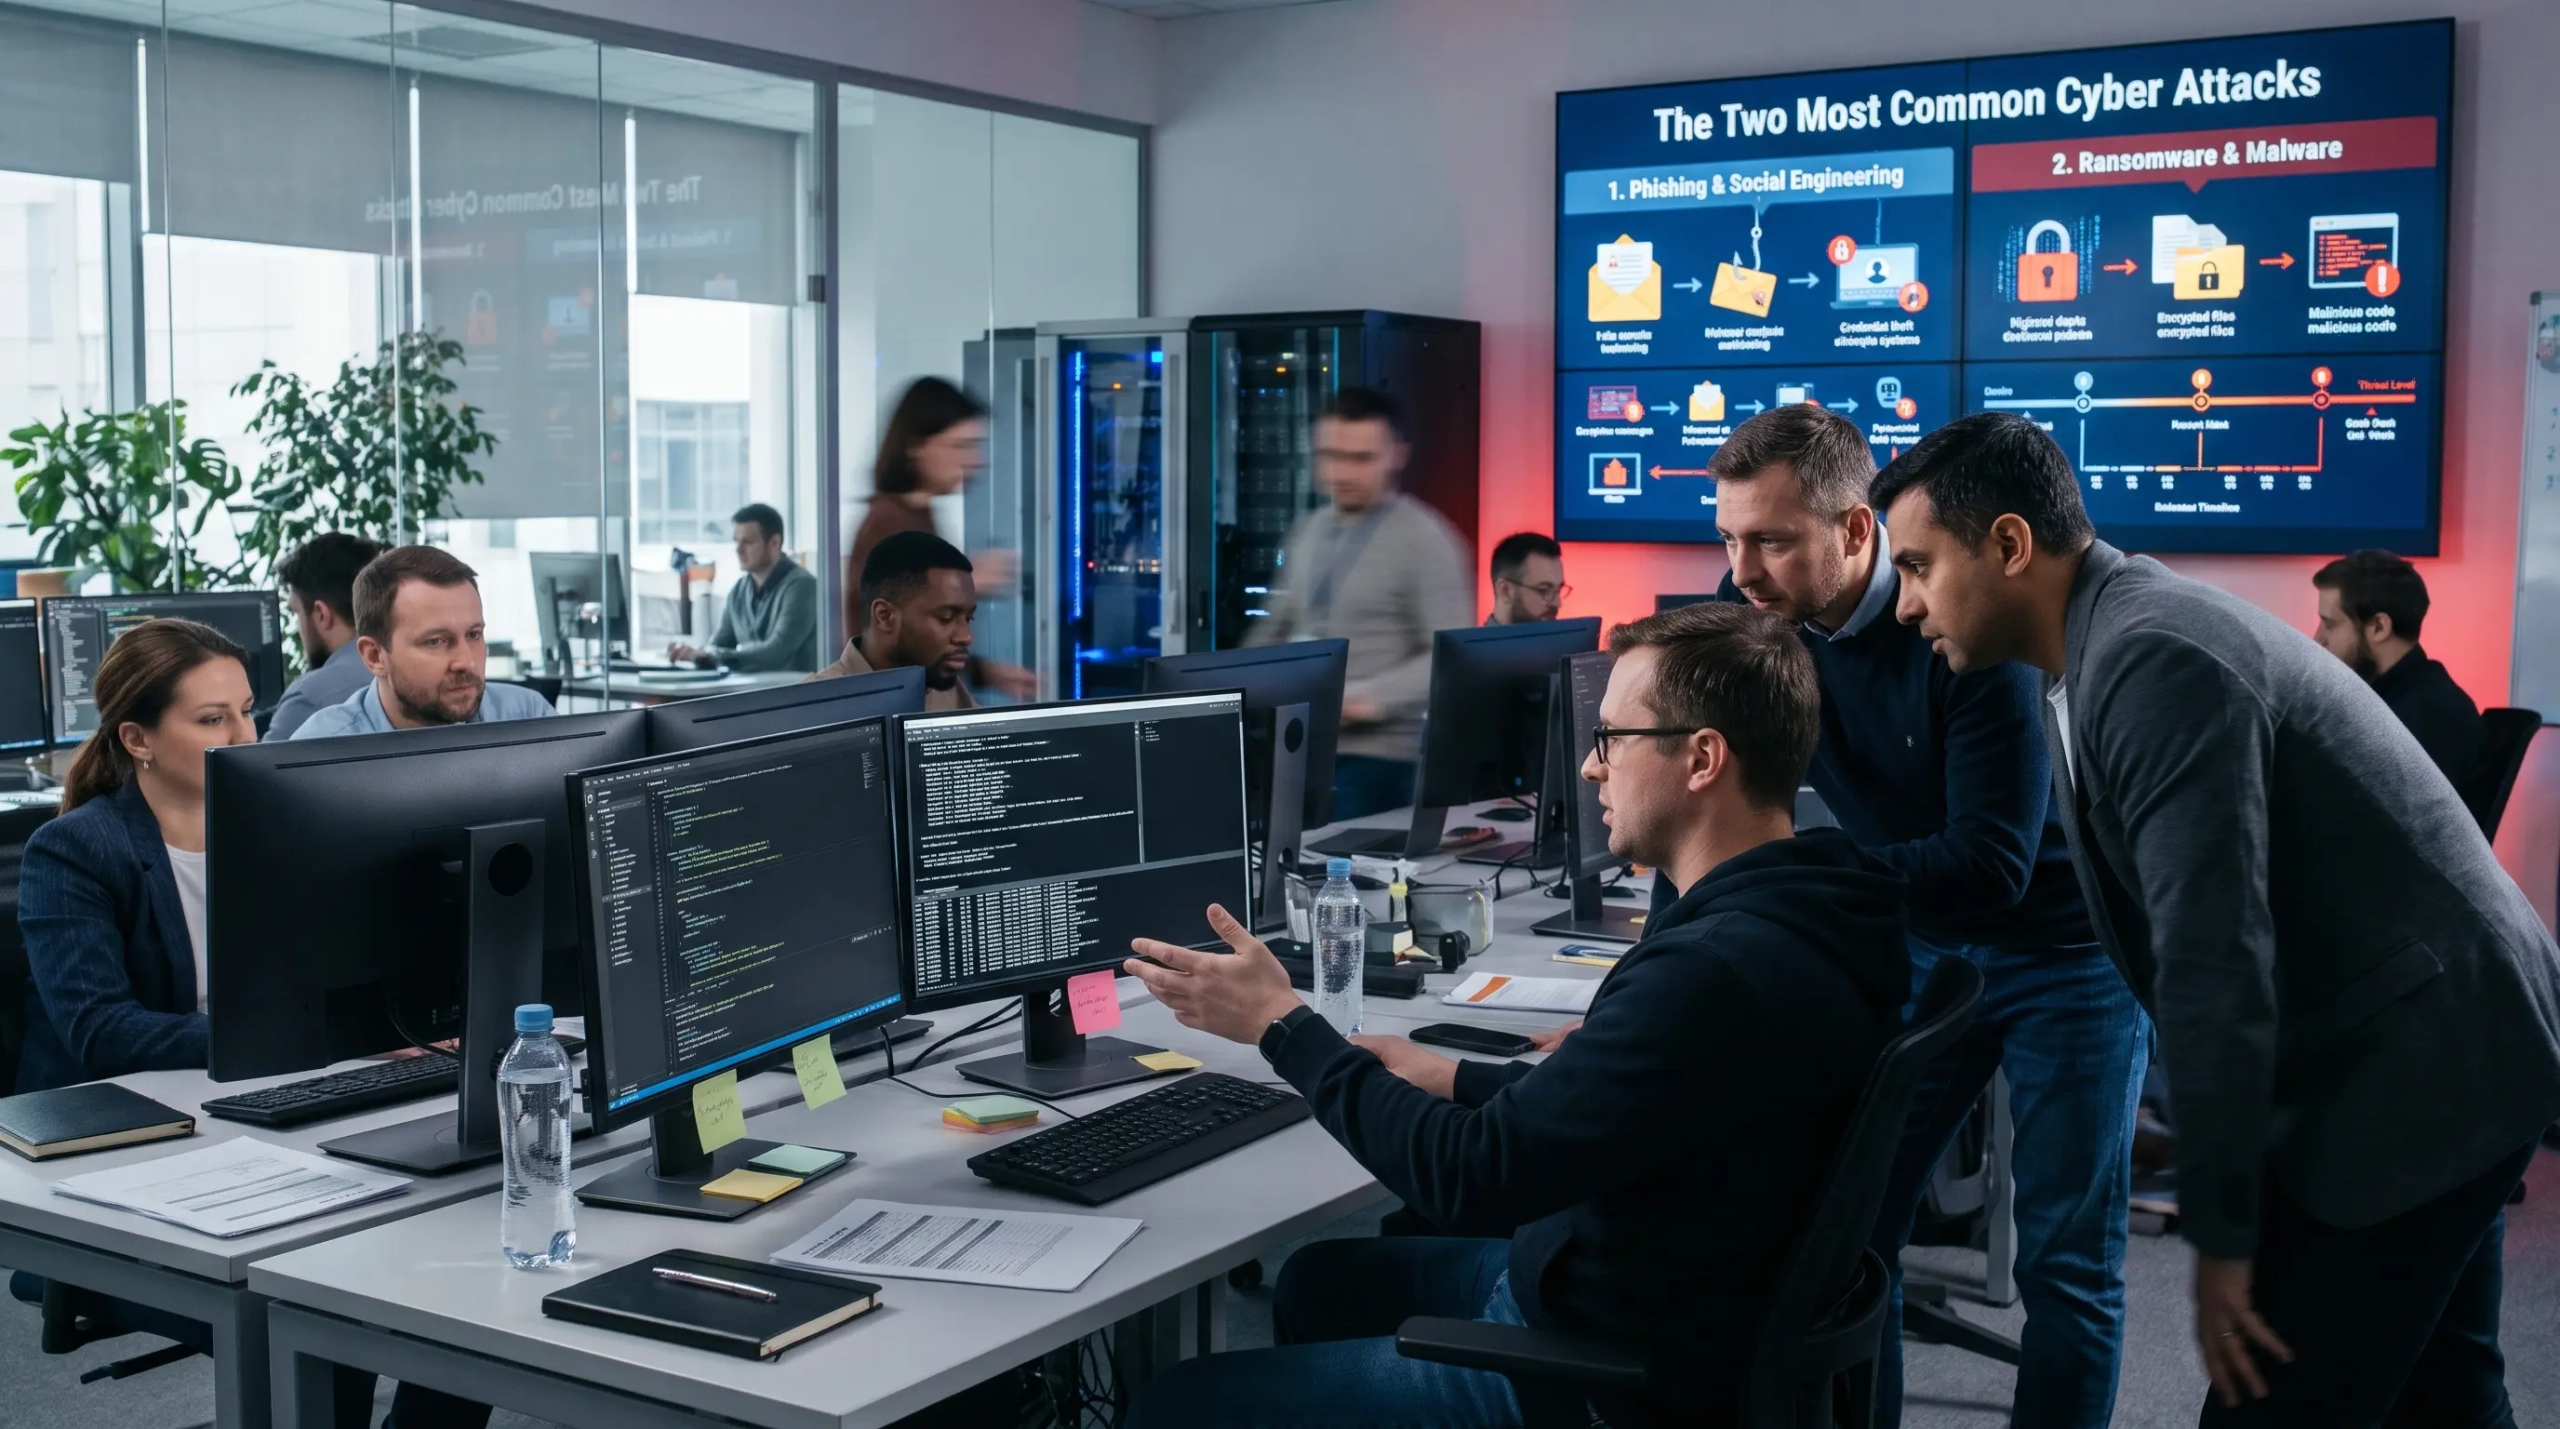
In the UK Cyber Security Breaches Survey 2025/2026, phishing and impersonation were the two most commonly reported breach or attack categories among businesses. Phishing was identified by 38% of businesses and impersonation by 12%. Those figures describe this survey’s population and definitions, not a universal ranking of every attack worldwide.
The report was published on 30 April 2026, with fieldwork conducted between August and December 2025 and questions about the previous twelve months. This guide uses that clearly defined evidence, then explains practical protections through an original small-business example. Sources were checked on 16 November 2026.
Key Takeaways
- State the population, period, and definition before calling an attack most common.
- Phishing and impersonation can overlap.
- Verify sensitive requests through a route you already trust.
- Use account protections alongside payment and approval procedures.
Which two attack categories lead in the cited survey?
The official UK survey’s Figure 4.4 places phishing first and impersonation second among all businesses covered by the estimates. The next listed category is devices targeted with viruses or other malware. This is a ranking of reported categories within the study, not a count of individual malicious messages.
| Survey category | Share of all businesses identifying it | Scope |
|---|---|---|
| Phishing | 38% | UK survey; previous twelve months |
| Impersonation in emails or online | 12% | Same population and reporting period |
Keep the denominator attached to the numbers. These are not percentages of all attacks, nor the chance that a particular email is malicious. A business may identify more than one category, so adding the two percentages does not produce a total share of affected businesses.
Different reports may measure incidents, successful breaches, monetary losses, or reports made to a particular service. Their top categories need not match. If someone gives a different pair, compare what the data counts before deciding that one list must be wrong.
The practical value of this evidence is prioritization with limits. It supports paying attention to deceptive messages and identities, but it does not make other threats irrelevant or establish the same ranking for your country, sector, or household.
How are phishing and impersonation different?
Phishing uses deceptive communications or destinations to induce an action, such as entering credentials, opening a harmful file, or providing information. In the survey, the phishing category covers fraudulent emails and fraudulent websites. The label describes a route used to deceive.
Impersonation concerns the identity an attacker presents: an organization, colleague, supplier, or other trusted contact. A request can impersonate someone and also be a phishing attempt. These are useful labels, but they are not perfectly separated boxes for every real incident.
A fake account-warning email may combine a familiar company’s branding with a credential-harvesting page. A supplier-payment scam may ask for a transfer without any login page or attachment. The first needs a safe route to the account; the second needs a reliable check of the payment instruction.
The National Cyber Security Centre’s business-payment-fraud guidance describes messages that appear to come from regular contacts and ask for payment to a different bank account. It identifies this kind of business email compromise as a practical risk to organizations.
Think about the requested decision rather than only the category name. Is someone asking you to reveal access, approve a payment, change a record, or install something? That question helps identify the check that matters.
Why can a convincing business request defeat a quick visual check?
An attacker may know a real project name or copy the style of an existing invoice. A compromised account can also send a message from a genuinely familiar address. Familiarity therefore cannot be the final approval step for a sensitive request.
Polished wording is equally limited. A message can be well written and still fraudulent. Conversely, a legitimate contact can make a spelling mistake. Inspecting presentation helps, but the transaction needs verification that does not depend entirely on the message being examined.
Use an independently established route: the provider’s app, a saved official address, or contact details already on file. If the message supplies a new telephone number for verification, calling it may simply keep you inside the same deception.
Our detailed phishing-email guide covers sender and link inspection. The additional business control here is deciding which actions must not be authorized from an unverified message, even when the message looks plausible.
Make that rule normal before a busy day arrives. Someone handling urgent orders should not have to invent a policy while a supposed manager insists that a transfer must happen immediately.
What should happen in a two-request example?
Consider an invented catering company preparing a weekend event. The owner receives two unrelated requests: an apparent payment-provider alert asking for a login, and a message apparently from an equipment supplier giving new bank details. Both refer to work the company really does.
Request one: the apparent account alert
The owner does not use the supplied sign-in link. Instead, they open the payment provider through an existing trusted route and check for the claimed issue. In this scenario, there is no matching notice. They report the suspicious message using the provider’s established process rather than replying with account information.
That result does not establish that every absent notification proves fraud. If uncertainty remains, the next step is the provider’s official support route. The important decision is to keep credentials out of the unverified path.
Request two: the changed bank details
The owner holds the payment and calls the supplier on a previously recorded number. In the example, the supplier confirms that the bank details have not changed. The company keeps the original payment record, preserves the message, and alerts the person responsible for security.
Notice why the first check was insufficient for the second request. Finding no malicious link would not establish that new payment details were genuine. The owner had to verify the instruction itself.
The expected outcome of this worked example is a documented decision for each request. It is not a promise that one call detects every scam. Verification needs a trustworthy contact route and a clear record of what was confirmed.
Which protections support the verification process?
Combine account protection with controls over sensitive changes. A stronger sign-in method can reduce account compromise, but it cannot approve a bank-detail change on your behalf. The person processing the request still needs a procedure.
NCSC’s small-organization email guidance recommends passkeys where supported and strong, unique passwords with two-step verification for relevant password-based access. Follow your provider’s current setup and recovery instructions, and protect recovery methods too.
Keep devices and applications updated, give people only the access they need, and maintain backups you can recover. These measures address different failure points; they do not remove the need to question unusual instructions.
- Specify who can approve payment-detail and account changes.
- Use existing contact records for independent verification.
- Allow staff to pause a request without being punished for delay.
- Record what was checked and report suspicious activity promptly.
Our passphrase guide explains one part of account protection. Use it alongside the provider’s supported authentication methods, rather than reusing a memorable password across business services.
Computer Security is related BestDigiBooks reading for a broader defensive routine. Prioritize the controls that protect your actual accounts and workflows instead of buying tools to match an abstract top-ten threat list.
What changes if someone already acted on the request?
Identify what happened: a link was opened, credentials were entered, a file was installed, information was disclosed, or a payment was made. Those are different incidents. Tell the person responsible for security promptly, even if the action feels embarrassing or the extent is uncertain.
If money was transferred, contact the bank immediately through an official route. NCSC’s payment-fraud guidance recommends contacting the bank and the organization’s IT or responsible person. Do not delay while trying to negotiate a refund with the suspicious sender.
If an account may be compromised, use the provider’s official recovery guidance and coordinate with the responsible person. Recovery may include securing access, reviewing sessions and settings, and checking what the account was used to do. Do not treat changing one password as proof that the incident is finished.
Preserve relevant messages and records in the way your organization’s response process requires. Report through the appropriate local or sector channels. Outside the UK, use the relevant services for your location rather than assuming a UK reporting route handles every case.
After the immediate response, review the decision that failed. Was a new bank account accepted without a callback? Did someone use a sign-in link because the official route was unclear? Repair that process so the lesson becomes a practical control.
Conclusion
Use a scoped answer: phishing and impersonation lead the categories reported in the cited UK survey, not necessarily every dataset. For your own business, choose one sensitive action today and define its independent verification step before the next urgent message arrives.
Frequently Asked Questions
Does low reported prevalence make ransomware unimportant?
No. Frequency and potential impact are different dimensions of risk. A less commonly identified event can still be highly disruptive for an affected organization. Keep appropriate backups, recovery planning, and security measures rather than choosing protections solely from the first two survey categories.
Can a telephone or video call be impersonation too?
Yes. A voice or familiar-looking participant is not sufficient on its own to authorize a sensitive change. For an unexpected instruction, return to an established contact route or agreed approval process. Apply the same decision rule across channels instead of trusting a request because it moved beyond email.